“Our scanner drowns us in false positives and we cannot upload code.”
Find the exploitable bugs, keep the code local.
The problem
- Most scanner findings are noise, and developers have stopped reading them.
- I cannot send our source code to a SaaS scanner or an AI assistant.
- We must report an actively exploited vulnerability within 24 hours and cannot tell which of our products use the component.
With INDAGO
- Findings are ranked by reachability and exported as SARIF; coding agents query the real call graph.
- A new CVE is matched to earlier internal write-ups and affected components in one search.
- Every confirm-or-kill decision is recorded for auditors.
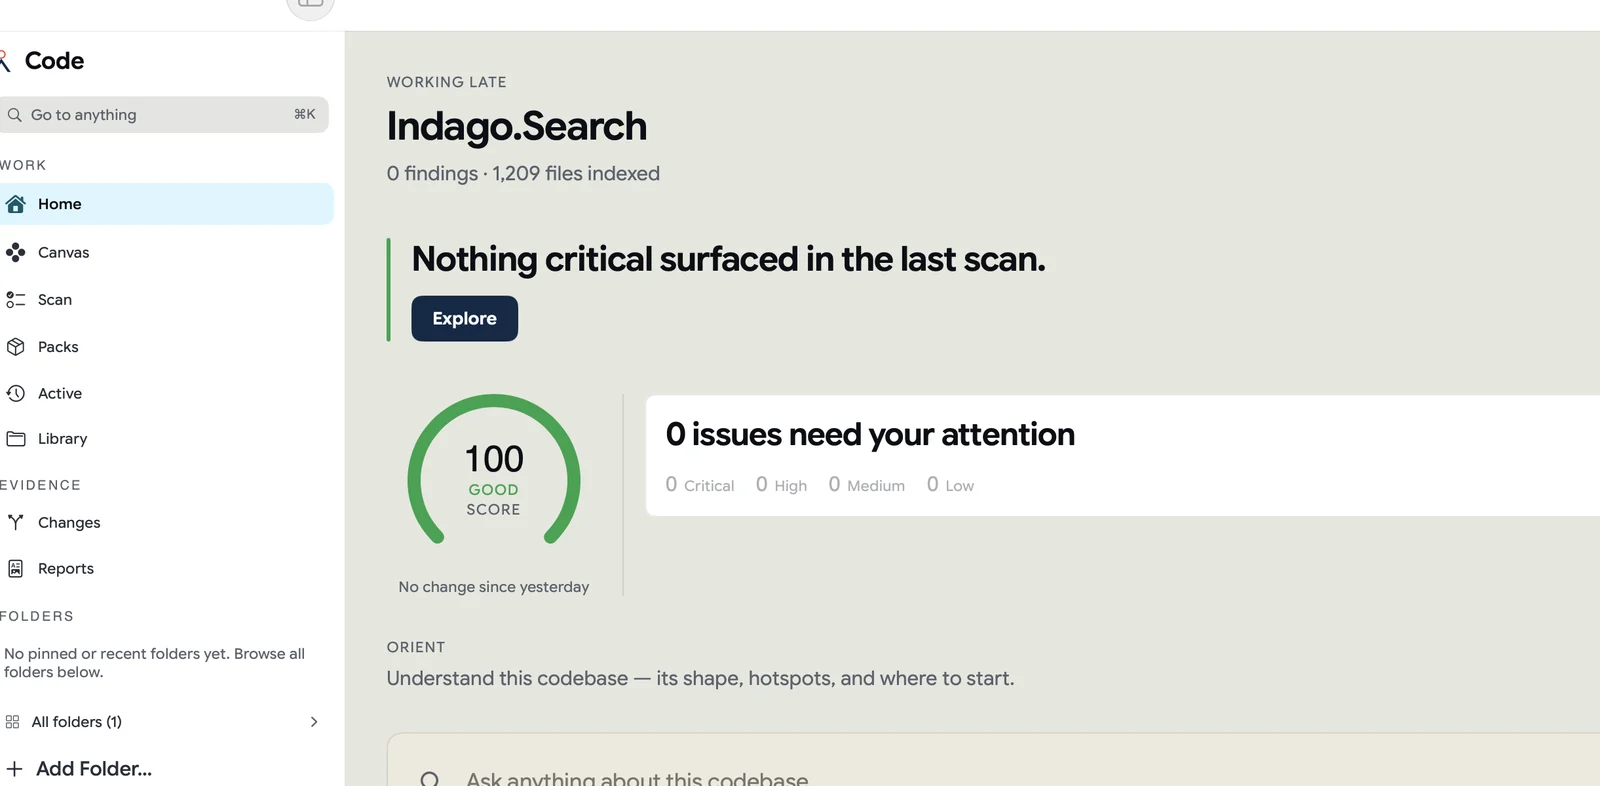
Real capture · Code home for a repository: score, findings and Ask-the-codebase.INDAGO Code 0.7.9 · a 1,209-file C# repository
Your setup. Free to start.
Start here · free
INDAGO Accelerate
A new CVE is matched to earlier internal write-ups and affected components in one search.
Get INDAGO — freeRecommended for you
INDAGO Code
Findings are ranked by reachability and exported as SARIF; coding agents query the real call graph.
Why your tools fall short.
×
Cloud SAST/SCA and AI assistants require uploading code, which regulated teams cannot do.
×
Pattern scanners without reachability analysis cannot separate exploitable from dormant findings.
×
Threat-intel reports, advisories and past post-mortems live in PDFs and wikis outside the code tooling.
NIS2 Art. 21Point (2)(e), security in acquisition, development and vulnerability handling.
Cyber Resilience ActRegulation (EU) 2024/2847: reporting obligations phase in from 2026.
How INDAGO answers.
Find it in a blink.
Your documents stay on your Mac.
macOS · Apple silicon · Signed and notarised