“We have 24 hours to report and the evidence is everywhere.”
Incident evidence in seconds.
- We have 24 hours to send an early warning and the evidence is spread over fifteen systems.
- The auditor wants proof we followed our own policy, and I have to grep three file shares.
- Our OT network is segregated, so none of the cloud security tools can even see it.
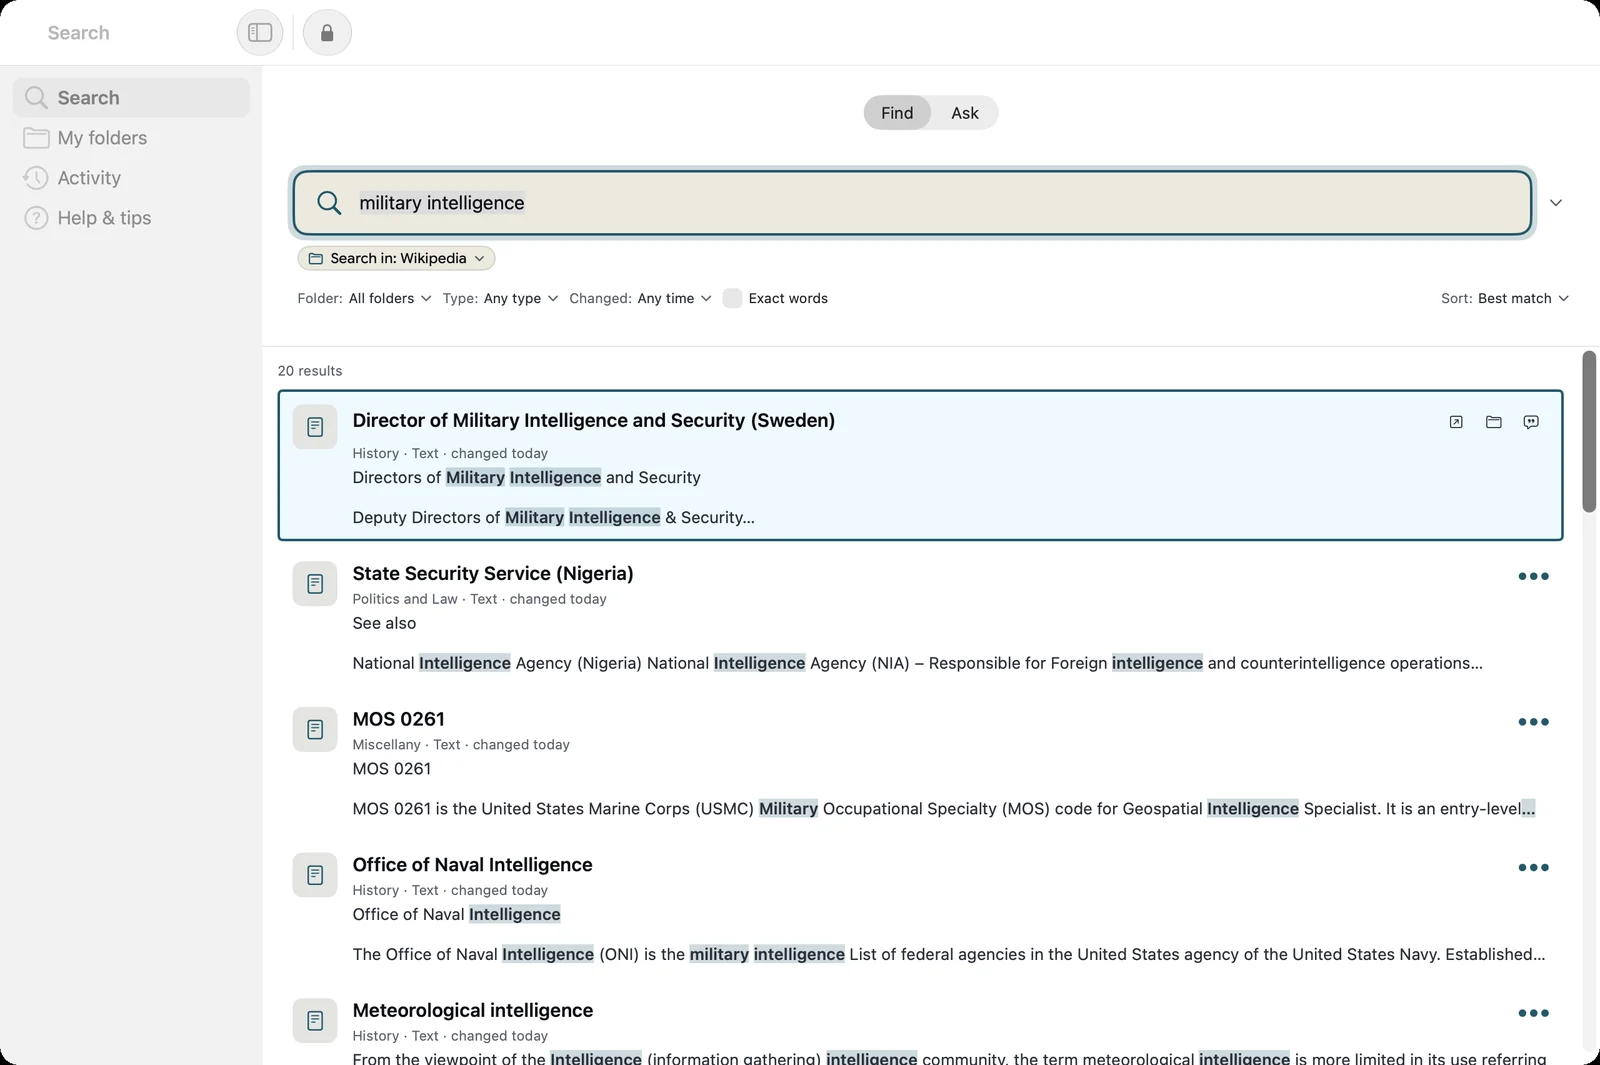
- During an incident the responder finds the applicable procedure and the last similar case in seconds, even on a segregated OT laptop.
- Evidence for each control is collected with citations and a verifiable record, ready for the auditor or the authority's final report.
- Internally developed OT/IT software is scanned on-premises and findings feed vulnerability handling evidence.
Your setup. Free to start.
INDAGO Accelerate
During an incident the responder finds the applicable procedure and the last similar case in seconds, even on a segregated OT laptop.
Get INDAGO — freeINDAGO Desktop
Evidence for each control is collected with citations and a verifiable record, ready for the auditor or the authority's final report.
Why your tools fall short.
GRC and ticketing platforms store structured controls but do not read the unstructured evidence documents themselves.
SIEM/log tools do not cover policies, contracts, manuals and scanned procedures.
Cloud-based AI is excluded for OT and for sectors with sovereignty obligations.
How INDAGO answers.
During an incident the responder finds the applicable procedure and the last similar case in seconds, even on a segregated OT laptop.
INDAGO DesktopEvidence for each control is collected with citations and a verifiable record, ready for the auditor or the authority's final report.
INDAGO CodeInternally developed OT/IT software is scanned on-premises and findings feed vulnerability handling evidence.
Find it in a blink.
Your documents stay on your Mac.
macOS · Apple silicon · Signed and notarised